SSO Isn’t Enough: Why Secure SSO Browsers Must Own the Session
Key Takeaways
- SSO verifies identity at login; it doesn't govern downloads, clipboard use, or tabs afterward.
- A secure SSO browser binds that identity to last-mile controls across apps and risk levels.
- Native browser-layer control sees the full session; extensions and network tools cover only part of it.
- Contractor and BYOD access show the gap first: IdP login works while the browser stays outside policy.
What browser SSO is built to solve
Single sign-on (SSO) is an authentication pattern that lets one trusted login open access to many related applications. In browser-based work, that usually means federated sign-in to SaaS and internal web apps through standards such as Security Assertion Markup Language (SAML) or OpenID Connect (OIDC).
Those protocols sit inside broader identity and access management (IAM). Multi-factor authentication (MFA) strengthens proof of who is signing in.
Federated identity links corporate directories to cloud apps. Zero Trust keeps asking whether that access still makes sense as context changes.
The security advantages are real: fewer passwords, centralized offboarding, and cleaner audit of authentication events. The tradeoff is concentration of risk. A stolen session or a weak post-login browser path can unlock many apps at once.
Browser setup still matters for classic integrated Windows authentication and intranet zones. Trusted sites, group policy, and browser URI allowlists help SSO fire cleanly. Those steps solve reachability and Kerberos or NTLM handshakes.
They do not, by themselves, decide what an authenticated user can download or paste once the app is open. That is why "secure SSO browser" searches often mix two jobs.
One is making SSO work in Chrome, Edge, or managed Windows environments. The other is governing the authenticated session after the handshake succeeds.
This guide focuses on the second job, because that is where enterprise SaaS risk now concentrates. Conditional access at the identity provider (IdP) still does important work at the front door. The open question is what happens after the green check.
Where SSO stops after a successful login
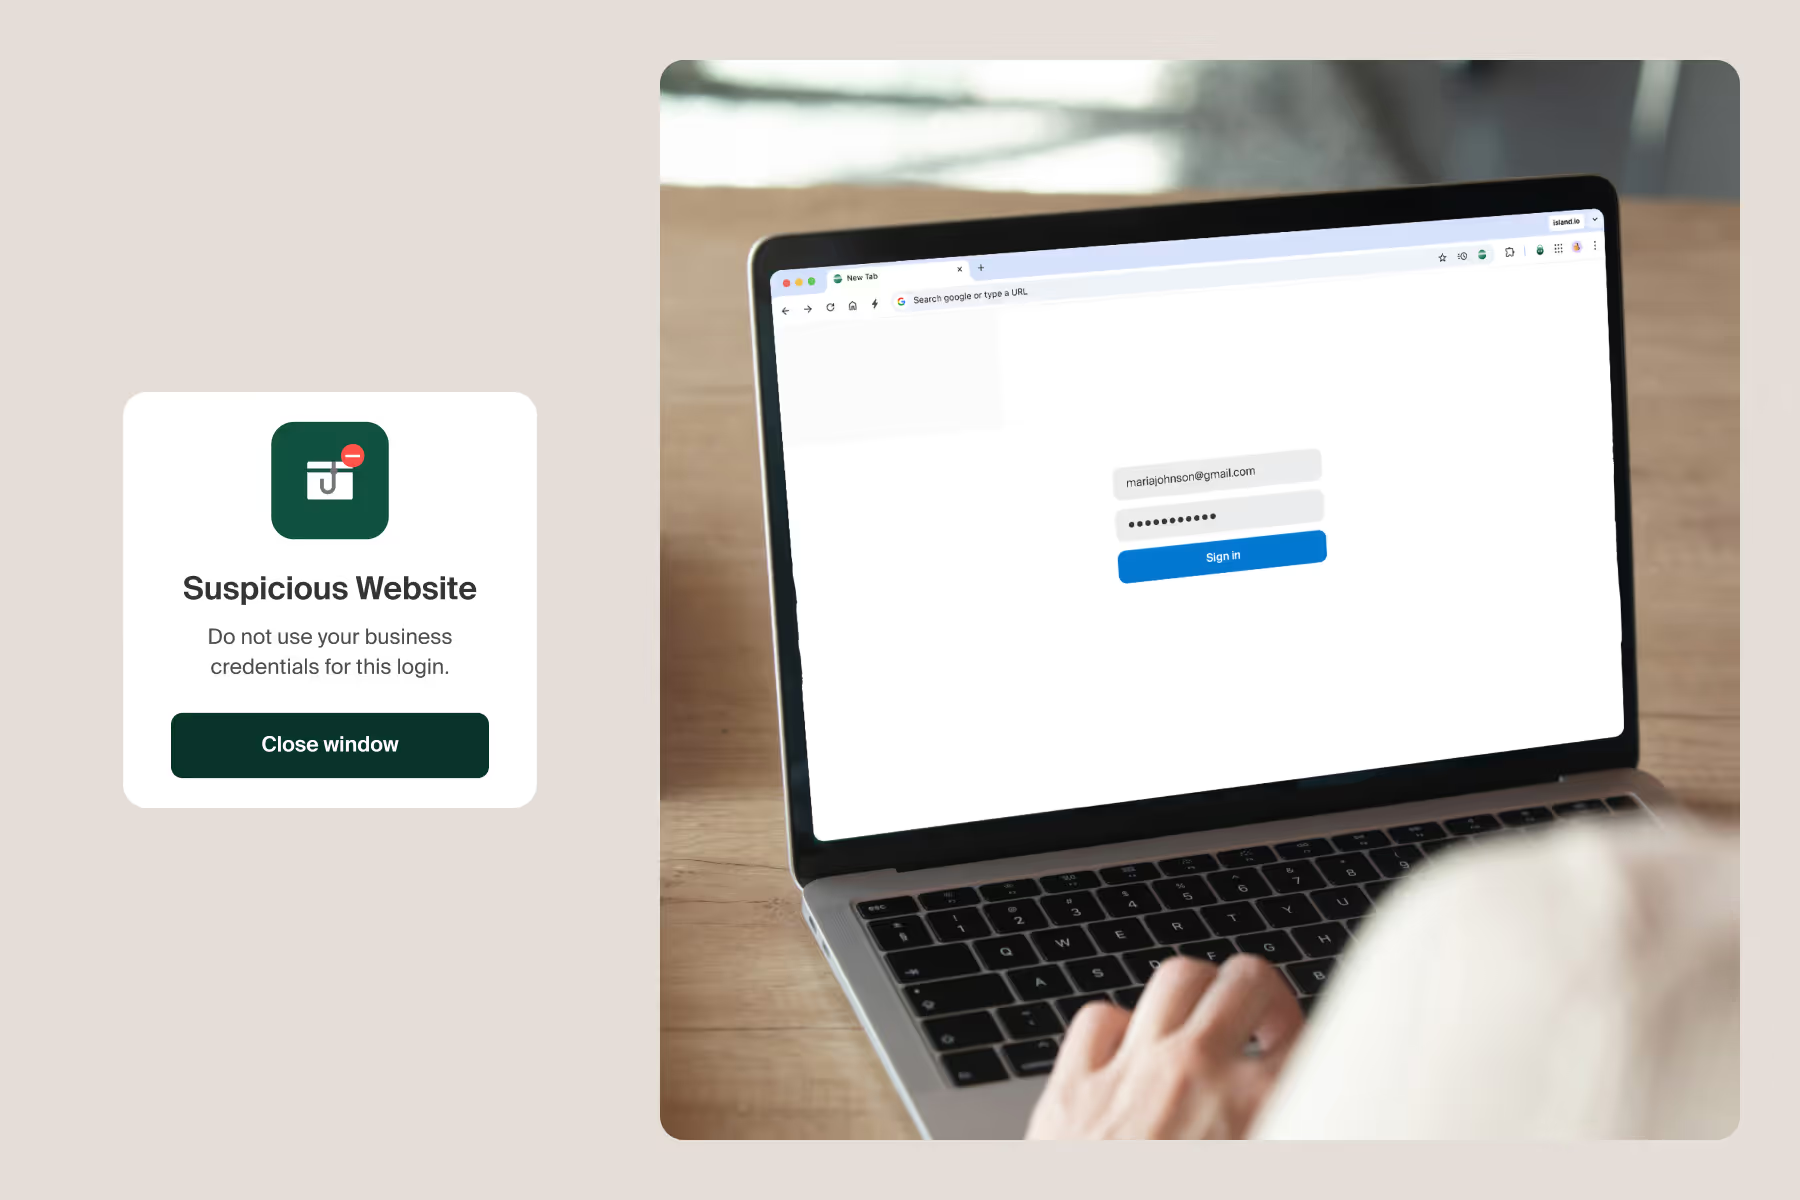
You know the frustration: the ticket isn't about a failed login. It's about what happened inside the browser once the session was live.
Most of your enterprise work is browser-mediated SaaS and web apps. Login is one moment in a long session of tabs, downloads, copy/paste, screen shares, and extensions.
Your IdP can gate entry based on user, device posture signals it can see, and risk scores. It rarely sees the hour that follows: data leaving a customer system tab into a personal drive, a contractor pasting records into chat, or a phishing overlay after authentication already succeeded.
That gap is easy to miss in architecture reviews. The identity project looks complete. Help desk queues tell a different story.
You still see exfiltration paths that skipped a failed login, shadow uploads from authenticated sessions, and investigations that stall because the browser stays opaque after the token is issued.
Verizon's 2025 Data Breach Investigations Report (DBIR) analysis still treats compromised credentials as a major initial access path, appearing in 22% of the breaches reviewed in that research. Strong SSO and MFA reduce front-door risk.
That is why identity programs often pair SSO with browser-layer thinking about compromised credentials. They don't automatically turn the browser session into a governed workspace.
None of these are good answers if the session after SSO is still a free-for-all. They're just the answers most stacks have.
Access patterns that stop short of the session
You didn't land here by ignoring security. You layered the best answers available when the problem looked different: manage the consumer browser, push third parties through VPN or VDI, and inspect traffic on the network path.
Those choices still shape how you compare what an enterprise browser is supposed to do next. Each pattern solved a real constraint. Each still leaves a hole the modern SaaS session can exploit day after day.
Three patterns still show up in many enterprise stacks:
- Managed consumer browser + IdP policies: Solved admin and authentication for a device-centric era, not full last-mile control after login.
- VPN and VDI for third parties: Solved untrusted-device access when policy couldn't live in the browser, at the cost of weight and help-desk load.
- Network inspection without last-mile control: Security service edge (SSE) and proxies still matter for destinations; many session actions still don't look like clean network events.
VDI solved the access problem of its era. The browser layer wasn't where policy could live then. Today that's where work happens, and your architecture needs to follow.
The shared limitation isn't that earlier approaches failed a test they should have passed. The modern SaaS session surfaced criteria those designs weren't built to own: identity-bound control of actions inside the page, not only authentication at the edge of the app.
What must be controlled after the token lands
If your request for proposal (RFP) stops at "supports SAML and OIDC," you're still buying a logon feature. A secure SSO browser has to keep ownership after the token lands, when the user is already inside the apps that hold the data.
That is the pivot many buyer guides understate when they treat seamless logon as the headline instead of the baseline. Three non-negotiables define that ownership:
- Identity continuity: Session context stays attached to actions, not only to the login event.
- Last-mile action control: Download, upload, clipboard, print, screenshot, and screen share follow app risk.
- Visibility with privacy: Enough audit of sensitive app activity to investigate, without turning personal tabs into blanket surveillance.
Market direction is catching up to that definition. Gartner predicts that by 2028, 25% of organizations will use secure enterprise browsers to enhance remote access and endpoint security.
The useful reading isn't "buy a category label." You need a control point that can sit on managed and unmanaged endpoints and govern the session where SaaS work runs. Seamless logon is necessary, but session ownership is what makes SSO security hold after login.
How browser security architectures compare
You can spend weeks scoring feature matrices and still miss the evaluation that matters: where policy executes when a user is already authenticated into customer systems, HR systems, or an internal admin console.
Feature checkboxes can look complete even while the session still leaks. For SSO-heavy environments, architecture usually falls into a clear hierarchy for native session control:
- Enterprise browser with built-in controls: Policy lives where users click, download, and paste, with identity context attached.
- Browser extensions on existing browsers: Faster to deploy and useful; depth varies, so treat extension-only designs carefully when full session ownership is required.
- Network or proxy-only controls: Strong for destinations and traffic patterns; weaker for last-mile actions that rarely become clean network events.
Cloud isolation can protect high-risk destinations and untrusted content. That is why isolation often appears beside extension models in browser architecture comparisons.
That pattern complements everyday SaaS SSO sessions. It isn't the same as owning the native user experience (UX) people use for routine work all day.
Isolation shines for risky links. It's a poor default for most authenticated hours in core business apps.
You feel this distinction in support load. When isolation is the default for ordinary SaaS, users notice lag, broken workflows, and "why does this feel different from my usual browser?" tickets.
When isolation is reserved for untrusted destinations and the daily workspace still feels familiar, adoption holds. The architecture choice isn't only about threat models. It's about whether security remains invisible enough that people keep working inside the governed path.
Many SSO RFPs still over-score IdP connectors and under-score session telemetry for the tabs after login. Ask vendors to show a policy decision on clipboard and download for a single SaaS app under the same SSO user.
A SAML screenshot proves logon. It doesn't prove session ownership. If the demo can't change a download or paste outcome mid-session without bouncing the user back through authentication, the evaluation is still a front door, not a workspace.
How Island connects SSO success to session control
When you need the IdP handshake and the hour after it to live in one environment, the product question gets concrete. In the Island Enterprise Browser, identity-aware access and last-mile controls sit in the same workspace rather than arriving as another tool after login.
Conditional access can assess identity, device, network, location, and application in the browser itself. Users still get seamless IdP SSO across the SaaS estate. Policy can then govern print, download, screenshot, and copy/paste against the same session context.
Application boundaries help keep sensitive data from sliding into the wrong tab. Security becomes a byproduct of how the environment is structured, not a second product someone has to remember to open.
That design shows up clearly for contractors and BYOD. Third parties can authenticate and reach the SaaS apps they need without defaulting most workflows to a full VDI stack.
Contractor access becomes a governed browser session instead of a long wait for a corporate image. Virtual desktops don't need to disappear overnight.
Many SaaS-heavy third-party use cases no longer need that weight as the default answer. Across enterprise deployments, the pattern is consistent: when policy moves into the browser environment, identity keeps meaning after the token lands.
If security doesn't live in the workspace, it rarely fully reaches the work.
What to pressure-test before calling a browser SSO-secure
Before you stamp "secure SSO" on a shortlist, pressure-test claims against the session, not the sales deck. Use the same discipline you bring to choosing an enterprise browser.
If you've lived through checkbox RFPs, you already know how easy it is to confuse integration screenshots with operational control. Your shortlist should survive a live session, not only a connector checklist.
- Does policy follow the session action, or only the auth event?
- Can the same SSO user get different last-mile controls by app risk?
- How are unmanaged devices handled without a second desktop stack by default?
- If people use generative AI in the browser, is paste and upload risk in scope after SSO?
Run those questions in a live pilot, not a slide. Pick one high-value SaaS app, one contractor persona, and one internal power user.
Watch what happens when each tries to export a file, paste a customer record, or open a second identity in a personal profile. The gaps that matter show up in minutes when the session is instrumented instead of when category labels are debated.
Also separate administration from ownership. Central policy push, extension allowlists, and device posture checks are necessary hygiene.
They still leave open whether the browser environment can enforce different outcomes for the same authenticated user across apps with different data sensitivity. If most apps inherit the same blunt allow-or-block posture after SSO, you either frustrate users or accept exceptions that become permanent.
The proving ground is rarely the hardest internal thick client. It's the embarrassing workflow you already know is over-controlled: contractor read-only SaaS access still forced through VDI because browser policy "can't do it."
If a candidate architecture can't change that story, it isn't owning the session. It's decorating the login.
See the session controls after SSO in practice
If you're evaluating this shift, schedule a walkthrough of post-login controls against your IdP and a real SaaS workflow. Request a demo.
FAQs
Why isn't SSO enough to secure browser-based work?
SSO verifies identity at login. It doesn't automatically stop a download from a finance app or a paste from a customer record into a personal tab after that login succeeds.
What should a secure SSO browser control after login?
Identity-aware policies on session actions such as file movement, copy/paste, screenshots, and application boundaries, tied to the same user context that authenticated.
How do enterprise browsers work with Entra ID or Okta?
They integrate with enterprise IdPs for seamless SSO, then keep enforcing conditional and last-mile controls throughout the browsing session. See the session ownership section above.
Can this approach support contractors without defaulting to VDI?
When policy lives in the browser environment, many third-party SaaS workflows can use governed access without shipping a full virtual desktop for most cases.
How is this different from locking down a consumer browser with enterprise policies alone?
Managed consumer browsers improve administration. An enterprise browser architecture makes security and access controls native to the workspace rather than external constraints only.
Island is defining the future of work for people and AI agents. Its enterprise agentic control plane helps organizations enable, govern, and audit agentic workforces alongside people. Island boosts productivity across devices, browsers, applications, networks, and data while protecting sensitive information, simplifying access, and helping enterprises scale AI safely.