Seasonal Surges, Shared Kiosks, and Franchise Data: What Retail Needs from an Enterprise Browser
Enforcing policy in the browser keeps customer and pricing data out of personal email, public AI tools, and shared devices — without slowing peak-season onboarding.
The most-used enterprise application in retail isn't the point-of-sale system — it's the browser. Store associates use it to check schedules, process returns, and look up inventory. Distribution center teams reach warehouse management portals through the browser; e-commerce teams and franchise operators use it to place orders and pull pricing from corporate systems.
Most of this work still runs in consumer browsers built for individual use, with no awareness of corporate policy, data sensitivity, or who should see what. Enterprise retail organizations are forced to compensate by surrounding the consumer browser with a complex and costly stack: SWGs, CASBs, DLP agents, VPNs, VDI, and extensions are all single-problem solutions that collectively compound cost, user friction, and operational overhead. AI only makes things more complicated while introducing potential new data risks.
The enterprise browser addresses all of these problems in a single, unified control plane. Security, compliance, and IT management are all embedded into the browser itself, at the exact point where work takes place. Here’s how the enterprise browser also handles some of the retail sector’s biggest IT headaches, including rapid short-term workforce expansion during peak retail periods and support for shared devices and kiosk terminals.
1. Seasonal headcount swings
Holiday hiring compresses months of onboarding into a few weeks. Thousands of temporary associates need scheduling, POS, and inventory access from their very first shift, often on personal phones and laptops, and that access has to end the day their contract does. Device provisioning, VPN configuration, and VDI capacity planning were built for a stable workforce on company-provisioned laptops, though, and typically require peak headcount pricing that leaves you paying for December’s workforce all year long.
How the enterprise browser solves short-term sales surge hiring:
- Self-service install on any device. Seasonal associates download the browser to their own phone or laptop and sign in with corporate credentials. There's no device to ship or image, no certificate installation, and no device profile to configure. Alternatively, the temp worker signs into company devices through their own securely segregated browser account.
- Identity-driven access and permissions. Temporary credentials come from the retailer's existing identity provider. Once a hire's role is set in the HR system, the browser grants exactly the applications that role needs, such as scheduling, POS, and inventory, with no per-user IT work.
- Work/personal separation on personal devices. Corporate data stays inside the managed browser workspace. Policies block copying, downloading, or moving it to personal sites, email, and public AI tools or chatbots.
- Instant, clean deprovisioning. In an enterprise browser, offboarding the worker in the HR system ends access immediately. Since no corporate data was saved to a BYOD device, there's nothing to wipe or recover; temporary hires instantly lose access to login credentials for any corporate kiosks or devices.
Evaluating an enterprise browser for seasonal hiring
Flexible infrastructure provisioning becomes possible when you make temporary associate access identity based instead of device based. No VDI capacity sits idle after the holidays, and no VPN rollout needs support during the busiest weeks of the year. If this is important to your organization, look closely at an enterprise browser’s licensing structure.
Ask vendors how their licensing models handle seasonal scaling. Are you locked into annual commitments based on peak headcount, or does licensing dynamically change based on actual usage? Some vendors charge per enrolled user, while others charge per concurrent session. The right model depends on whether you’re a retailer that hires in one large holiday surge or turns over staff steadily through the year.
2. Shared and kiosk devices on the sales floor and in the warehouse
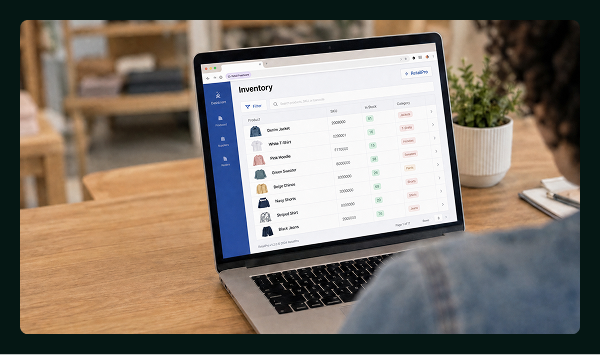
Retail hardware rarely belongs to one person. Associates share back-office workstations and floor tablets, and distribution centers run stations locked into kiosk configurations. A morning associate, an afternoon department manager, and a weekend seasonal hire may all use the same machine with different access rights. When sessions don't end cleanly, one user's authenticated access to a refund portal or HR system can carry into the next shift, potentially allowing unintended access to sensitive applications or risking compliance issues when activity logs attribute actions to the wrong user.
How an enterprise browser helps solve identity management and secure access on shared devices:
- Policies follow the person, not the machine. Each associate signs in with their own credentials through SSO, and the browser applies entitlements based on their role in the identity provider. A seasonal hire and a department manager on the same back-office workstation see different applications and operate under different data controls.
- Step-up authentication for sensitive applications. The browser can require an additional MFA challenge before a user reaches sensitive applications like payment administration or authorizing high-dollar return items. This adds a checkpoint on devices that have multiple users every day.
- Corporate data stays out of local storage. Downloads, saves, and copy-paste can be restricted by policy, so files pulled from an inventory or loyalty system don't sit on a shared machine for the next user to find.
- Per-user audit trails. Because activity is tied to an authenticated identity instead of a device, logs attribute each action to the person who took it. This matters for loss prevention and compliance on shared hardware.
- Imaging and central management for kiosk fleets. Kiosk deployments include the browser in the device imaging process, and policies are updated from a cloud console across every store and distribution center. Those policies include which extensions can run, so an AI writing assistant or page summarizer installed by one associate can’t read the refund portal or HR record the next associate opens on the same workstation.
Evaluating an enterprise browser for shared devices and kiosks
The two major things to investigate for this use case are session handling and platform coverage. Ask vendors how their enterprise browser user sessions end, whether credentials and cached data are cleared between users, and how quickly the next associate can sign in.
Platform coverage may also be important: store and warehouse fleets often mix Windows workstations, ChromeOS devices, and Linux-based kiosks with tablets on the floor, and the browser's controls can only function on supported systems.
3. Data segregation across franchises and locations
IT real estate for national and global retail brands often includes corporate-owned stores, franchisees, and vendors who all use the same ordering portals, planogram tools, and invoicing dashboards. Standard browser security controls risk blurring corporate, franchise, and regional boundaries between locations, applications, and appropriate user access. A franchise operator should see only their location's catalog, pricing, and orders. Corporate merchandising and finance teams need a network-wide view, and vendors need narrow, task-specific access.
Beyond role-based concerns, external parties frequently connect from their own devices on networks you don’t control, and customer data privacy obligations such as CCPA and GDPR are a particular challenge if your retail operation does business across borders.
How the enterprise browser solves data segregation across different retail locations and franchises:
- Partner access without device management or VPN. Franchise operators and vendors install the browser on their own devices without an IT ticket and sign in with partner credentials. Integrated ZTNA gives them access to private applications, such as ordering portals and planogram tools, without VPN configuration or additional network agents.
- Identity-based policies scoped to the partner. Policies determine which applications each external user can reach and what they can do inside them, based on their identity and group membership.
- Controls on what leaves the application. The browser can block exports, downloads, copy-paste, printing, and uploads to AI tools, and session controls prevent bulk extraction. For example, a franchise operator can use the ordering portal but can’t export master SKU lists or paste wholesale pricing into a chatbot to build their own forecast.
- DLP and masking for customer data. DLP detectors flag loyalty account numbers, payment details, and other PII regardless of the originating application, and the same detection applies to prompts and file uploads bound for AI tools. Masking hides sensitive fields until a user needs them, and each unmasking event is logged — crucial for compliance in situations where locations in different countries carry different privacy obligations. Customer data can’t be sent to an outside model provider.
- Audit logs for partner activity. Every action by an external user is logged and can flow to the SIEM, giving compliance teams evidence of what partners accessed and did.
- Context-aware access. Device posture and geolocation checks let access decisions reflect where and on what an operator is connecting.
The rest of the evaluation
The Retail Browser Buyer's Guide goes much deeper into the considerations and capabilities you should bring to evaluating an enterprise browser, including PCI DSS scope reduction, POS integration, and loss prevention integration. It compares enterprise browsers with remote browser isolation, VDI, and security service edge solutions, and explains why traditional browser security approaches can’t completely defend you when granting, managing, and revoking access in a retail environment. The guide also covers additional sector-specific challenges like enabling safe AI adoption, reducing VDI costs, keeping stores running during ransomware or outages, and extending zero trust to a distributed workforce.
Take the full checklist into your next vendor conversation
Retail IT and security leaders will find the latest research and analysis around the enterprise browser solution space, plus a structured way to test enterprise browser vendors against the requirements that matter most in their environment. Read the full guide for analyst perspectives from Gartner, Frost & Sullivan, and GigaOm, and to get the full evaluation checklist covering crucial enterprise browser capabilities and integrations.
Download the guide to build your evaluation before the next peak-season sales rush begins.
FAQs
Can seasonal workers use an enterprise browser on their personal phones and laptops?
Yes. Seasonal associates download the enterprise browser to their own devices and sign in with temporary credentials from the retailer's identity provider. There's no device to ship or image and no certificate or device profile to install. Corporate data stays inside the managed browser workspace, and policies block copying, downloading, or moving data to personal sites and email.
Can an enterprise browser require extra authentication for sensitive applications on shared devices?
Yes. The browser can require an additional MFA challenge before a user reaches sensitive applications like payment administration or HR portals. On workstations and tablets used by many associates each day, that step-up authentication adds a checkpoint beyond the initial sign-in.
Does every enterprise browser support the operating systems used in stores and warehouses?
No. Retail fleets often mix Windows workstations, ChromeOS devices, and Linux-based kiosks with iOS and Android tablets on the sales floor. An enterprise browser's controls function only on the platforms it supports, so retailers should confirm coverage for every device type in their stores and distribution centers before selecting a vendor.
Can an enterprise browser help retailers meet customer privacy obligations such as CCPA and GDPR?
Yes. DLP detectors flag loyalty account numbers, payment details, and other PII regardless of which application the data comes from. Masking hides sensitive customer fields until a user needs them, and each unmasking event is logged. Together with audit logs of user activity, these controls give compliance teams evidence of how customer data was accessed across locations with different privacy requirements.
Island is defining the future of work for people and AI agents. Its enterprise agentic control plane helps organizations enable, govern, and audit agentic workforces alongside people. Island boosts productivity across devices, browsers, applications, networks, and data while protecting sensitive information, simplifying access, and helping enterprises scale AI safely.