AI Security Software For Employee AI Usage: A Buyer's Guide
Learn what AI security software needs to cover, the criteria that separate real protection from a checklist, and the questions worth asking vendors.
Key takeaways
- Employee AI usage now spans at least five distinct entry points: browser-based chat tools, agentic browsers, installed desktop apps, browser extensions, and API/MCP connections. Most security tools were built to see only one or two of them.
- Buying criteria should center on where enforcement actually happens (browser, endpoint, network) and whether a tool can distinguish sanctioned corporate AI accounts from personal ones, not on a generic feature checklist.
- Blocking AI outright doesn't reduce risk; it pushes usage into unmonitored "shadow AI," where nearly half of employees admit to using tools against policy and most hide it from IT.
- The durable model is governed enablement: giving employees safe, monitored access to AI rather than restricting it. This requires enforcement built into the layer where prompts and pastes occur, not layered on top after the fact.
- Evaluate vendors on architecture first: ask how visibility, policy, and data protection are implemented technically, then compare features.
Introduction
Most enterprise security leaders didn't choose this coverage problem. It opened up underneath them as employees adopted generative AI tools faster than procurement or security teams could evaluate them. The tools already in the stack, including network proxies, endpoint DLP, and CASB, were built for a different era of traffic.
The relevant question now is which kind of AI security software works. This guide walks through what AI security software needs to cover, the technical criteria that separate real coverage from a checklist, and the questions worth asking any vendor before signing a contract.
Why employee AI usage outgrew existing security tools
Where existing security tools stop covering AI
Generative AI didn't arrive through a new procurement process. It arrived through a browser tab, an extension, or an app employees already had permission to install. According to McKinsey's 2025 workplace report, 78% of organizations now have active generative AI initiatives. The Stanford HAI 2025 AI Index echoes that scale, finding that 78% of organizations reported using AI in 2024, up from 55% the year before. That growth outpaced the ability of legacy DLP and CASB tools to keep up, because those tools were designed to inspect structured data moving through known channels, not freeform prompts typed into a chat window.
The result is the data protection gap AI created: security teams have visibility into file transfers and email attachments, but very little into what an employee pastes into a public AI tool.
How shadow AI became the default state
"Shadow AI," AI use that happens without employer approval or visibility, has become the default state in most organizations rather than the exception. A global study by KPMG and the University of Melbourne, covering roughly 48,000 people, found that close to half of employees admit to using AI against workplace policy. Fifty-seven percent actively hide their AI use from employers. That pattern reflects an architecture failure: employees have easy access to AI, and security teams lack comparable visibility into how it's used. As one Island analysis put it, shadow AI is an architecture problem rather than a people problem: the tools available to workers evolved faster than the systems meant to govern them.
What AI security software needs to cover
The nine entry points employees use AI through
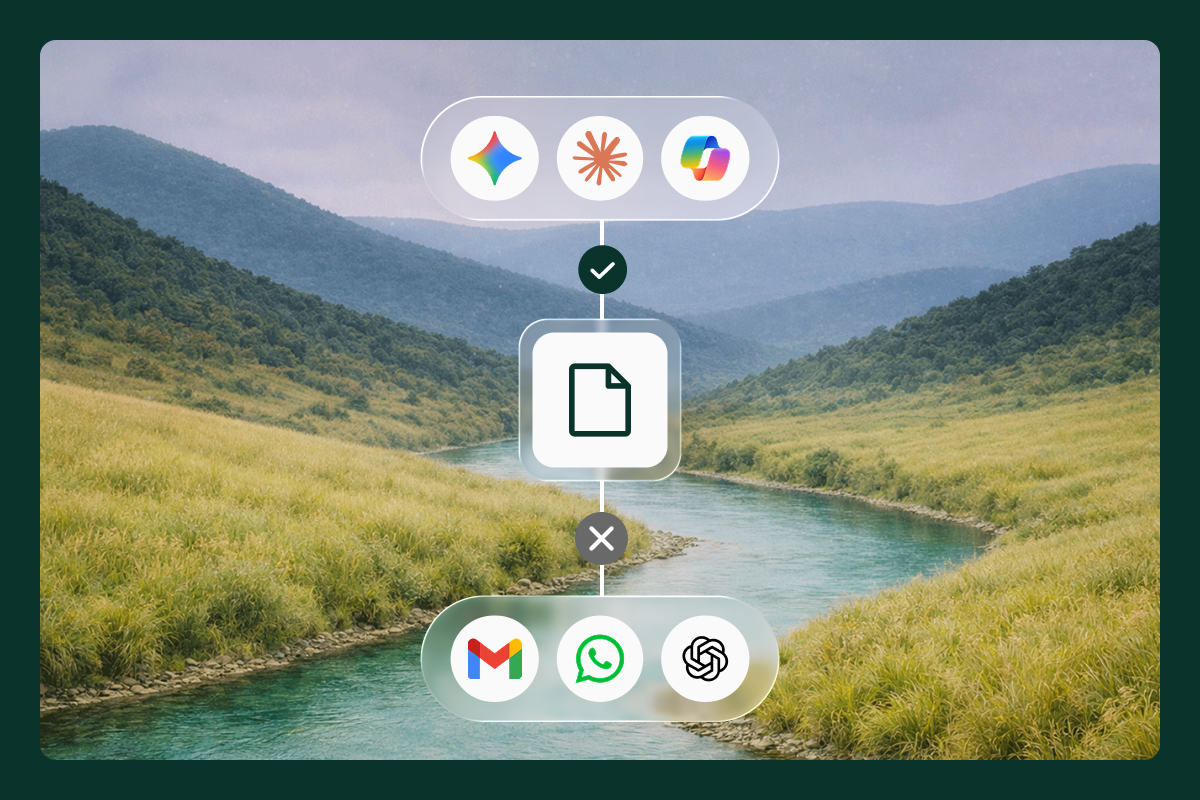
Any AI security software has to account for nine distinct entry points where employees interact with AI: standard browser-based tools like ChatGPT or Claude, agentic browsers that act on a user's behalf, installed desktop applications, browser extensions that inject AI functionality into other sites, and API or MCP (Model Context Protocol) connections used by developers and automated agents. A tool that only monitors network traffic will miss activity inside an agentic browser session. A tool that only manages installed applications will miss a browser extension quietly summarizing a Google Doc. Coverage needs to span all five entry points; partial coverage is a vendor choice, not a technical limitation.
Personal vs. corporate account blind spots
One of the most common blind spots is the personal-versus-corporate account distinction. An employee using ChatGPT through a company-issued account with data controls enabled is a very different risk than the same employee logged into a personal account on the same site. According to Gartner's survey of 302 cybersecurity leaders, 69% suspect or have confirmed employees using prohibited public generative AI tools, often because the tool in front of them can't tell which account is which.
Prompts, pastes, uploads, and agentic/MCP activity
Coverage also needs to extend beyond simple site blocking to the content of the interaction itself: what's typed into a prompt, pasted from a clipboard, uploaded as a file, or passed through an autonomous agent acting on a connected API. Microsoft's 2025 Work Trend Index found that 75% of knowledge workers now use AI on the job, with 46% having started in just the past six months. That means most of this activity is recent, high-volume, and largely unreviewed.
Core capabilities to evaluate
Visibility: seeing usage before governing it
Visibility has to come before enforcement, because a sound policy can't cover activity that hasn't been seen. Island's own deployment data illustrates the scale of this problem: one enterprise found 243 distinct AI products in active use across its workforce, against just 6 that had been formally sanctioned. That blind spot only became visible once browser-level monitoring was in place, since network logs and endpoint agents hadn't surfaced it.
Enforcement at the point of interaction
Visibility alone isn't enough. Enforcement needs to happen at the point where the risky action occurs, the moment a prompt is submitted or a file is uploaded, not after the fact in a log review. This is the core argument behind the enforcement gap in AI governance: policies that exist only on paper, without a technical mechanism to apply them in real time, don't change behavior.
Data protection built for unstructured prompts
Traditional DLP tools were tuned to catch structured patterns: credit card numbers, social security formats, specific keywords. Prompts to AI tools are unstructured and conversational, which means DLP built for how data moves today needs to understand context and intent instead of matching static string patterns. A buyer's guide worth using should test this directly: submit a realistic prompt containing sensitive context, in plain language, and see whether the tool catches it.
Policy that scales without rebuilding from scratch
As new AI tools and agent frameworks appear monthly, policy needs to scale by category and behavior rather than requiring a rule rewrite for every new vendor that shows up.
Questions to ask vendors during evaluation
Coverage across browser, desktop, extensions, network
Ask vendors to demonstrate coverage across all the entry points above, not just the one their product was originally built for.
How the tool distinguishes corporate from personal AI accounts
Ask specifically how the product differentiates a sanctioned corporate AI login from a personal one on the same domain, and what happens automatically when it detects the latter.
Time to deploy and policy migration effort
Ask how long deployment takes and what happens to existing DLP and CASB policies. Do they need to be rebuilt, or can they be extended?
Reporting and SIEM integration
Ask whether activity data integrates with existing SIEM and reporting workflows, so AI usage becomes part of standard security operations rather than a separate silo.
Also ask directly where AI acceptable use policies fail without enforcement, and whether the vendor's approach is meant to sit on top of existing endpoint protection or replace parts of it. That distinction is covered in more detail when layering AI governance on existing endpoint protection.
Buying the enablement model, not the blocking model
Why governed access outperforms restriction
Blanket blocking of AI tools tends to produce the same outcome shadow IT did a decade ago: employees route around the restriction using personal devices, personal accounts, or unmanaged browser tabs. The research bears this out: the National Cybersecurity Alliance found 65% of employees already use AI at work, 58% received no formal training on it, and 43% admitted sharing sensitive details with an AI tool. Restriction doesn't remove that behavior. It removes visibility into it.
Enterprise AI security without the productivity tradeoff means giving employees sanctioned, monitored paths to the AI tools they're already reaching for.
What this looks like day to day for security teams
In practice, this shifts security teams from a blocking posture to a monitoring-and-guardrails posture: sanctioned AI accounts get full access with data protection controls active, unsanctioned tools get flagged or restricted based on risk, and none of it depends on employees remembering a policy document. This is what Island's research calls a visibility problem, not a blocking problem: once you can see usage, governing it becomes a matter of policy tuning rather than a cat-and-mouse game with new tools.
How Island fits
Island builds AI governance into the browser, desktop, and network layers where employee AI activity happens, rather than adding a separate monitoring layer after the fact. Island AI Protect unifies visibility across all five entry points under one policy engine, distinguishing sanctioned corporate accounts from personal ones and applying data protection at the point of prompt, paste, or upload. That architecture is the basis for Island's approach to enterprise AI: governance that lets security teams say yes to AI usage with controls attached, instead of defaulting to blocking it and losing visibility altogether.
Conclusion
Employee AI usage grew faster than the tools meant to govern it, leaving security teams with visibility into file transfers and email but not into prompts and pastes. Closing that gap requires software built to see all five entry points, distinguish corporate accounts from personal ones, and enforce policy at the moment data leaves.
The vendors worth evaluating are the ones that can demonstrate this technically, not just describe it in a feature list. Governed enablement, not blanket blocking, is what lets security teams say yes to AI while keeping the controls that matter in place.
FAQs
Does AI security software replace our existing DLP and CASB investments, or sit alongside them?
It depends on architecture. Tools that add a monitoring layer on top of existing infrastructure typically coexist with current DLP and CASB deployments but add integration overhead. Tools like Island that build enforcement into the browser layer itself can extend or absorb policies that used to live in separate DLP and CASB products, reducing the number of systems that need separate rule sets for the same risk. Ask vendors directly whether their model is additive or consolidating, since that affects both cost and operational complexity.
How long does deployment typically take?
Deployment time depends heavily on where enforcement happens. Network-based tools often require infrastructure changes and can take months to roll out fully. Browser-based approaches, including Island, generally deploy faster because they extend an application employees already use daily rather than requiring new network routing or endpoint agent rollouts. Ask any vendor for a reference deployment timeline with an organization of comparable size before assuming a number.
Can this kind of software distinguish between an employee using ChatGPT for work versus a personal account on the same device?
Yes, if it's built to. This is one of the most important evaluation criteria in this guide: tools that operate at the browser or identity layer can differentiate sanctioned corporate AI logins from personal accounts on the same domain and apply different policies to each. Tools that only inspect network traffic often can't make this distinction, which is why 69% of security leaders in Gartner's survey suspect or have confirmed prohibited AI tool use they can't fully account for.
Will blocking AI tools outright reduce our exposure while we evaluate vendors?
Not durably. Blocking tends to push usage into unmonitored channels rather than eliminating it. The KPMG and University of Melbourne study found that 57% of employees already hide their AI use from employers, and blocking increases the incentive to do so on personal devices or accounts. A better interim step is visibility: turn on monitoring to see actual usage patterns before deciding what to restrict, since actual usage is often larger than IT assumes.
Does adopting AI security software require rewriting our acceptable use policy?
Policy documents alone don't create enforcement. Evaluate the software on whether it can technically apply the policy you already have, rather than restate it in writing. If your current AI acceptable use policy has no enforcement mechanism behind it, that's worth addressing regardless of which vendor you choose. See where AI acceptable use policies fail without a technical backstop.
How does this fit with EDR and endpoint protection we already have deployed?
Most AI security software is designed to layer on top of existing endpoint protection rather than replace it, since EDR and AI governance solve different problems: one focuses on malware and system integrity, the other on data leaving through prompts, pastes, and uploads. Ask vendors specifically how their product interacts with your current EDR stack; this is covered in more detail in layering AI governance on existing endpoint protection.
What does "coverage" mean when a vendor claims to monitor AI usage?
Ask them to define it against the five entry points: browser-based tools, agentic browsers, installed desktop apps, browser extensions, and API/MCP connections. A vendor that monitors only one or two of these can still legitimately claim to offer "AI monitoring," so the specific claim matters more than the general one. Request a live demonstration across all five rather than relying on a feature list.
Island is defining the future of work for people and AI agents. Its enterprise agentic control plane helps organizations enable, govern, and audit agentic workforces alongside people. Island boosts productivity across devices, browsers, applications, networks, and data while protecting sensitive information, simplifying access, and helping enterprises scale AI safely.